By Sameer Mehra
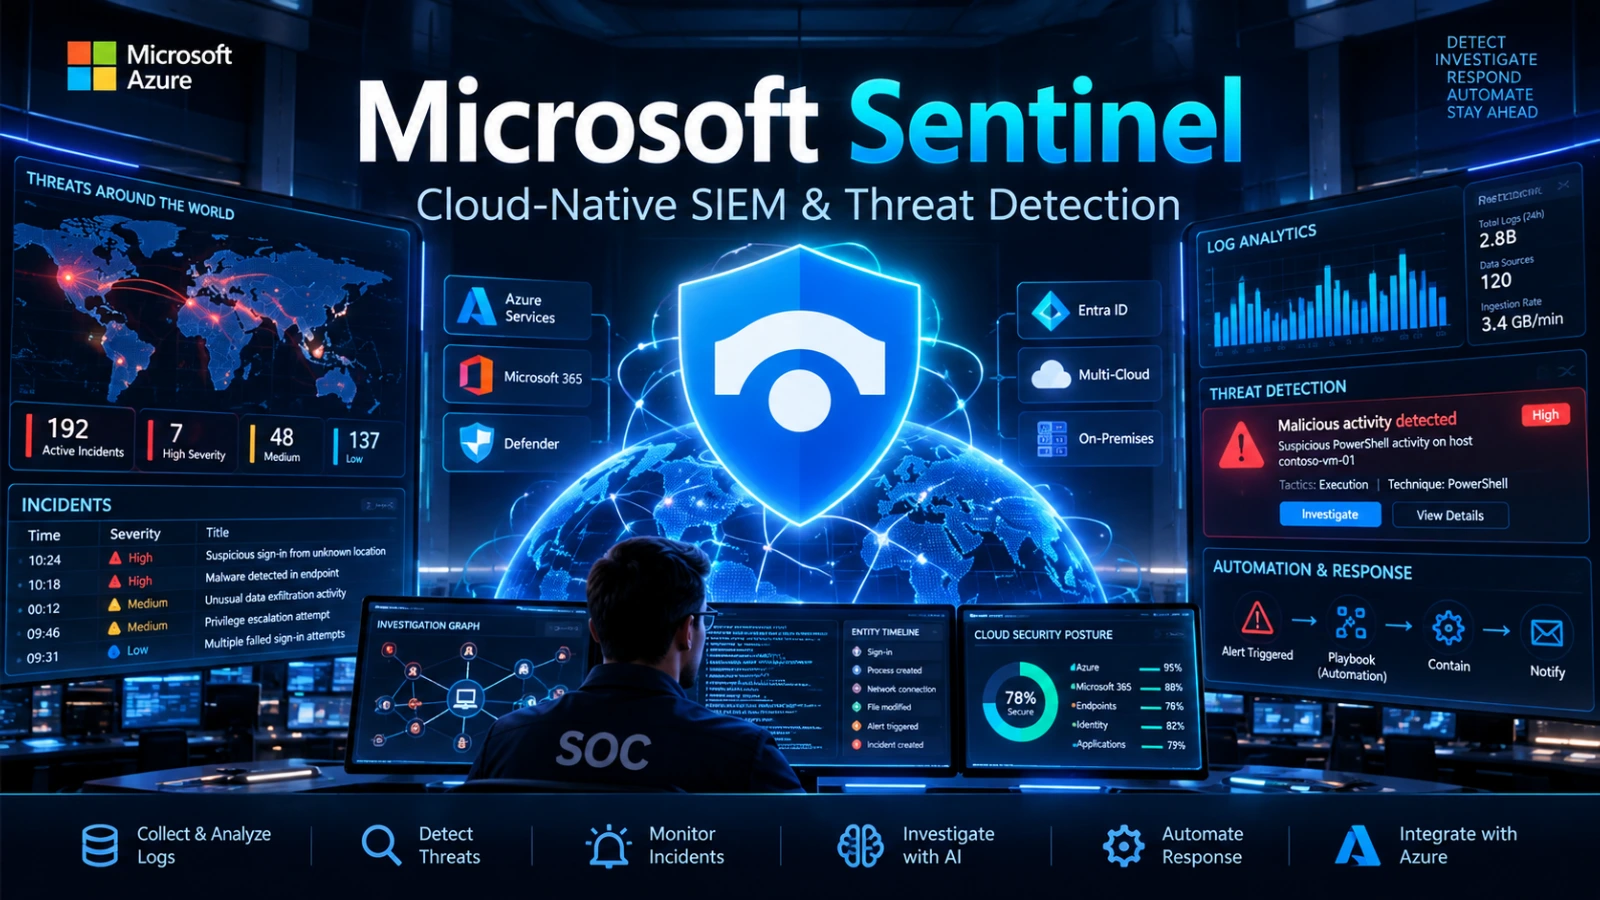
Build a strong foundation in Microsoft Sentinel and understand how modern Security Operations Centers use SIEM technology to collect, analyze, detect, investigate, and respond to security threats. This beginner-focused course explains SIEM fundamentals before introducing Microsoft Sentinel as a cloud-native security operations platform. Learners explore how Sentinel ingests security data through data connectors, stores and queries logs using Log Analytics and KQL, visualizes information through workbooks, detects suspicious activity using analytics rules, supports threat hunting and incident investigation, and automates responses using playbooks. The course also explains when Microsoft Sentinel is appropriate for cloud, multi-cloud, hybrid, and on-premises environments, as well as how it works alongside Azure Monitor, Log Analytics, and Microsoft Defender for Cloud.